fail2ban reads the logs and bans addresses that behave like attackers, at the firewall, for every application and SSH.
| Jail | Bans | For |
|---|---|---|
| sshd | 5 failed SSH or SFTP logins in 10 minutes | 1 hour |
| Kept hitting the limits | Addresses that keep hitting the protection limits (about 150 times in 2 minutes) | 1 hour |
| Scanners | 4 requests for typical weak spots (.env, .git, wp-config backups, shells) in 10 minutes | 1 day |
| Repeat offenders (recidive) | Addresses banned 5 times in a day | 1 week |
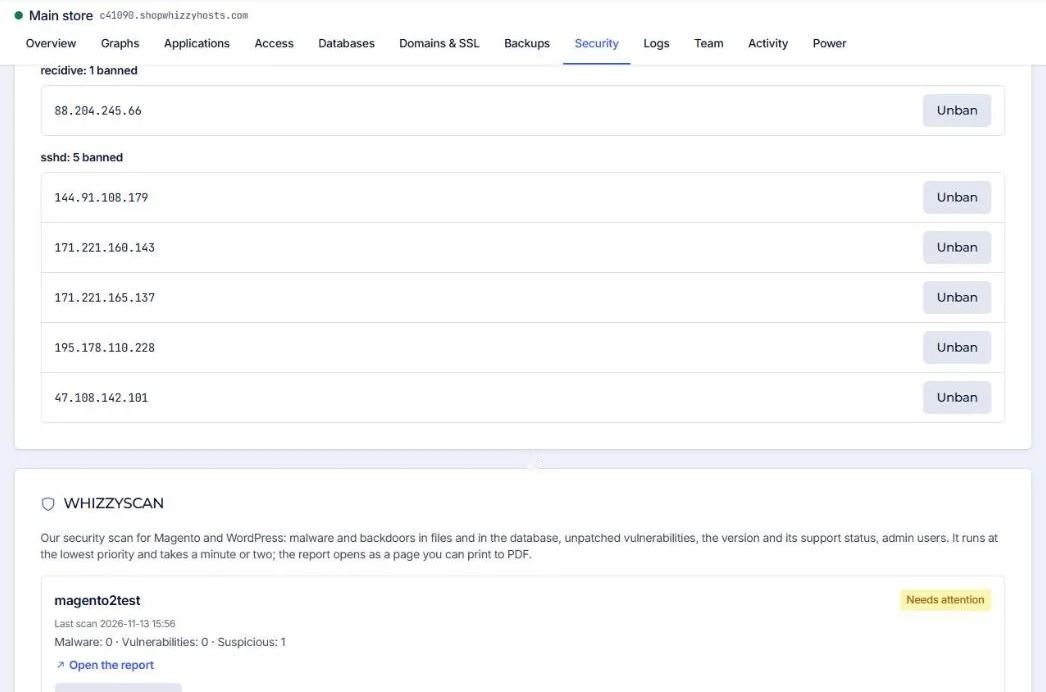
Unban an address
Security tab, find the address in its jail and press Unban. If a colleague keeps getting banned for SFTP, check their client uses the right key or password and stops after a failure.
Our platform's addresses are never banned.
Did this solve it? If not, tell us what you see and we look at your server.
Open a ticket