Every application gets a free Let's Encrypt certificate covering its domains. Certificates renew on their own about a month before they expire.
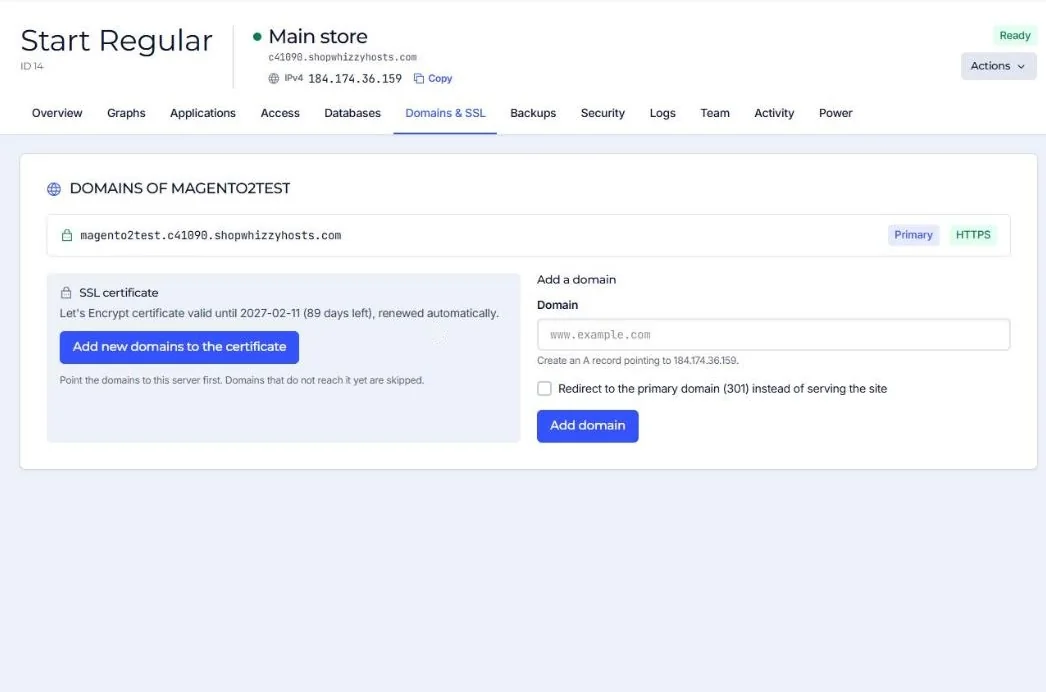
How issuing works
- The server checks that each domain really reaches it over HTTP.
- Domains that do not reach it yet are skipped and listed, so one forgotten DNS record never blocks the others.
- Let's Encrypt validates the domains and the certificate is installed. nginx reloads without downtime.
Using your own certificate
Need an EV/OV certificate or a wildcard from your provider? Open a ticket with the certificate and its chain; we install it for you.
Behind Cloudflare with the orange cloud on, the certificate still issues: Cloudflare passes the validation request through. Use SSL mode Full (strict) in Cloudflare.
Certificate does not issue? See The SSL certificate does not issue.
Did this solve it? If not, tell us what you see and we look at your server.
Open a ticket