
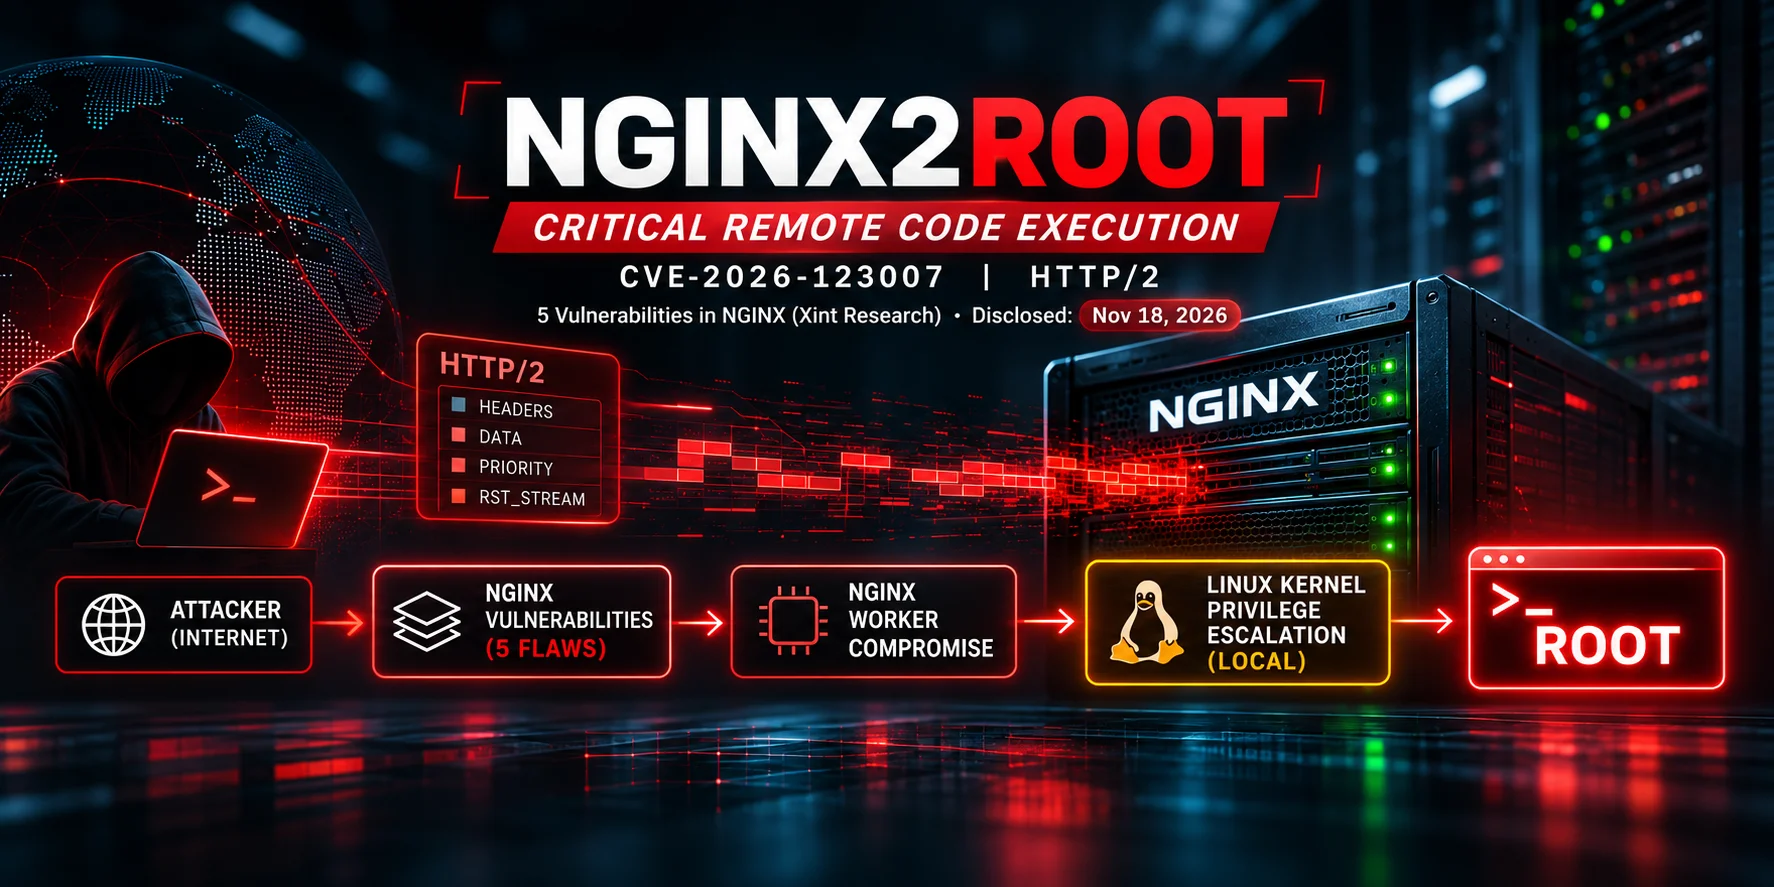
We have turned off HTTP/2 on every ShopWhizzy server we host and manage, as the first protection against nginx2root, five critical nginx vulnerabilities disclosed on November 18, 2026. If your store runs on our servers, there is nothing you need to do.
What nginx2root is
nginx2root is the name researchers gave to five memory-corruption flaws in nginx, published together with fixes by the nginx team on November 18. Each one can let an attacker run code on the server without logging in, with the privileges of the nginx worker process. The most widespread, CVE-2026-123007, is in the HTTP/2 code and affects every nginx release from 1.9.5 (2015) up to 1.31.8. A second one, CVE-2026-123633, also needs HTTP/2. The other three (CVE-2026-123634, CVE-2026-121810 and CVE-2026-113425) only apply to specific features: a dynamic resolver with proxying, HTTP/3 and the mail proxy.
The researchers also showed that, combined with a separate Linux kernel flaw, the attack can lead to full control of the server.
What we did
The fixed versions are nginx 1.30.7 and 1.31.9. At the time of writing, the packages that many Linux distributions ship for older nginx versions have no fix yet. So we did the thing that closes the door right away: we turned off HTTP/2 on every server we host and manage, testing the configuration before each reload, so there was no downtime. This blocks CVE-2026-123007 and CVE-2026-123633.
What changes for your store
Almost nothing. Your store is still served over HTTPS, and browsers simply use HTTP/1.1 instead of HTTP/2. On most stores the difference in speed is too small to notice.
What comes next
Turning off HTTP/2 is a mitigation, not the final fix. We are moving our servers to a fixed nginx version and reviewing the three features that HTTP/2 does not cover. Once a server is upgraded, HTTP/2 can be switched back on. We will update this post as that progresses.
Not hosted with us?
- Check your version. Run
nginx -v. Anything older than 1.30.7 (stable) or 1.31.9 (mainline) is affected. - Upgrade nginx, or ask your hosting provider to do it today. Some Linux distributions fix older versions without changing the version number, so check your provider's security notice.
- Until then, turn HTTP/2 off. On nginx older than 1.25.1, remove
http2from the listen lines (for examplelisten 443 ssl;). On 1.25.1 or newer, addhttp2 off;to each server block. Then test the configuration and reload nginx.
Technical details are in the nginx security advisories and in the researchers' write-up.


